All Categories
Featured
Table of Contents
The need for cloud infrastructure soars as the IT market grows, increasing the intricacy of property tracking and handling resources. Platform, DevOps and SRE engineers are essential in handling these environments, optimizing operations, and preparing for the future. According to Gartner, by 2025, over 90% of breaches in the cloud will have a root cause of avoidable misconfigurations or mistakes by end users.
Think: a way to arrangement, manage, govern, and manage their infrastructure even in a multi-cloud and multi-IaC world. Here's why cloud asset management is a game-changer for contemporary engineering teams. Cloud suppliers like AWS and Google focus on information security, but companies remain responsible for constant security enhancements. The cloud's dynamic nature makes it challenging for security groups to track and safeguard all properties.
If multiple team members release cloud resources individually, maintaining a total inventory of the resources ends up being tough, compromising security concepts, cost optimization, and security steps. Here are some of the difficulties faced by teams struggling with cloud possession management: Cloud environments constantly alter, with brand-new possessions being provisioned and decommissioned regularly.
In a hybrid cloud environment, different groups might use AWS, Azure, or GCP, requiring various tools for insights. Typically, no single tool provides a unified multi-cloud dashboard, making it challenging to maintain a detailed cloud possession inventory. As an outcome, PowerShell/Bash scripts are typically utilized, or the job is done manually.
This can make getting a detailed view of the security posture difficult, making it challenging to react to threats effectively. Without a correct tag management system, figuring out ownership, usage, and maintenance of cloud resources is challenging. Irregular tagging complicates cloud cost management and responsibility. One team might tag a virtual machine as "Environment: Production," while another utilizes "Prod," and some resources may lack tags entirely.
Refining Cloud Asset Management FrameworksIs Current Enterprise Budget Ready for 2026?
IaC tools streamline cloud resource provisioning, however this ease complicates monitoring user activities and tracking resource modifications. An RBAC policy governing what can be provisioned and what is off-limits based upon user roles is vital. Disparities occur if a DevOps engineer inventories cloud possessions for cost preparation, however somebody changes the instance size of 5 VMs without updating the IaC code.
Embracing CAM can spell big ROI, plus supply: The main benefit of tracking cloud assets is attaining total exposure of all resources that deliver cloud services. This extensive view allows accurate asset lifecycle management, making sure that properties are effectively kept track of, preserved, and optimized throughout their lifespan. The system aggregates data from AWS EC2 circumstances, Azure VMs, and Google Cloud Compute Instances into a single dashboard, enabling IT administrators to view all calculate resources, monitor their statuses, and ensure correct tagging and use.
However a robust cloud property inventory service does not simply list your resources; it offers a wealth of information about each possession: Resource type and specificationsCreation date and last modified timestampAssociated tags and metadataOwnership and access permissionsCost and usage metricsRelationships and dependencies with other assetsThis detailed information is essential for making notified choices about resource allocation, security measures, and cost management techniques.
To manage the surge, the website uses on-demand scaling with a cloud supplier like AWS. As traffic spikes, extra servers (EC2 instances) automatically launch to manage the increased load.
By acquiring an extensive understanding of their cloud property stock, companies can make educated decisions on security procedures, improving their general security posture. For example, a financial services business that shops sensitive customer information on cloud platforms such as AWS, Azure, and Google Cloud. To ensure robust security, they need a clear list of the assets and their configuration.
Streamlining IT Resources to Maximize Enterprise Efficiency
Organizations needs to execute procedures for continuously keeping an eye on and identifying misconfigurations in work to maintain a safe and secure environment. A few examples of misconfigurations in cloud resources include opening important ports such as database ports, SSH ports, RDP ports, etc, to the internet without restricting IPs, publicly accessible S3 buckets, or granting excessive permissions to IAM policies.
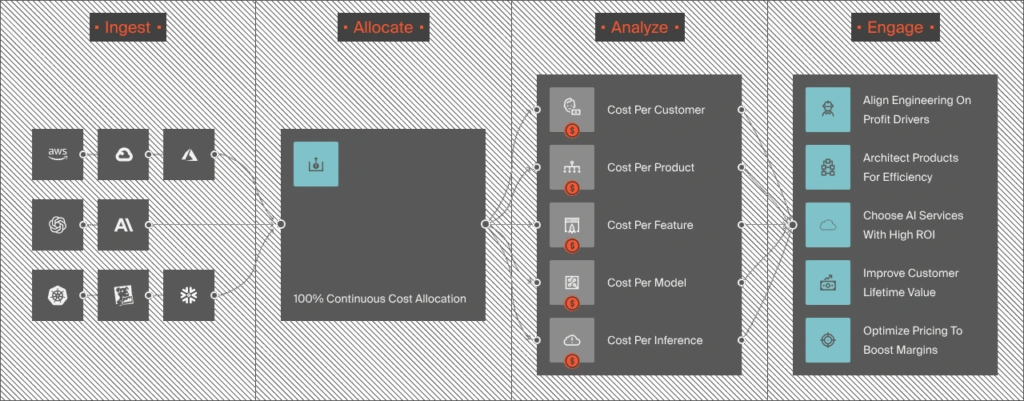
At the exact same time, it empowers DevOps to ramp Infrastructure-as-Code up quickly and to develop and deploy cloud facilities securely and regularly within organizational policies. Firefly is a Cloud Property Management software solution that assists DevOps, Platform Engineering, and SRE teams streamline their cloud management using Infrastructure-as-Code (IaC), which lowers cloud intricacy, improves property effectiveness, and constructs a reputable platform.
Firefly supports cloud service providers like AWS, GCP, K8s Clusters, DataDog, GitHub, Akamai, Okta, Terraform, Pulumi, and more, making it an efficient piece of cloud asset management software application for most of the cloud landscape. Firefly helps you manage your entire multi-cloud footprint.

Latest Posts
Top Strategies for Better IT Resource Optimization
Using Performance Metrics to Boost Cloud ROI
Next-Gen IT Asset Management for Cost Control